The specified network name is no longer available. (0x80070040) when trying to read HttpRequest Body using ReadToEndAsync()
New issue <!- ->
Содержание
ifmorrison opened this issue
Apr 8, 2016
· 13 comments
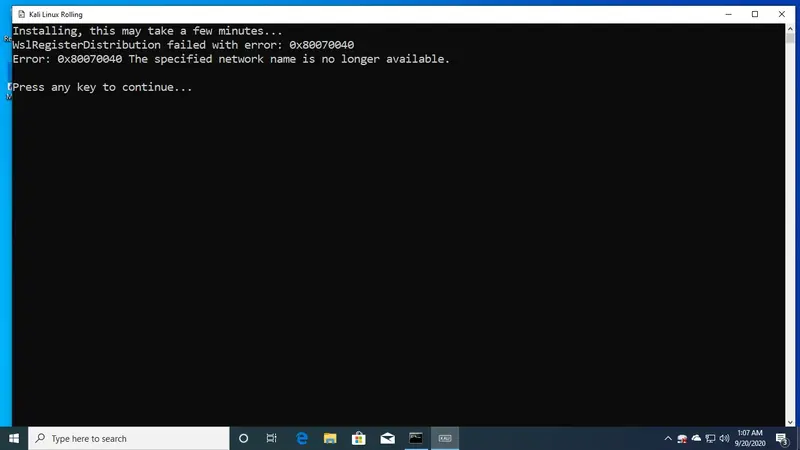
In this tutorial, we are going to learn how to solve Error: 0x80070040 The specified network name is no longer available in Windows 10 WSL 2.
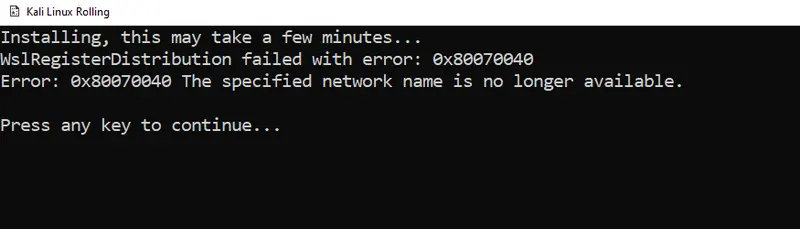
Installing, this may take a few minutes...
WslRegisterDistribution failed with error: 0x80070040
Error: 0x80070040 The specified network name is no longer available.
Press any key to continue...
For example, in my Windows 10 PC, I have a Kali Linux distribution that fails to install with the error: The specified network name is no longer available.
wsl --set-default-version 1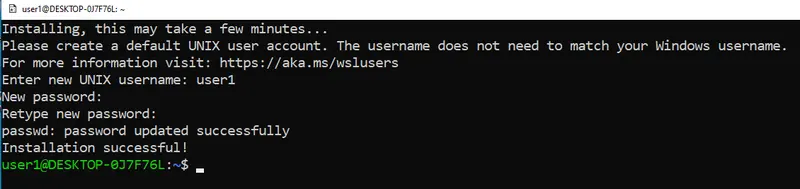
wsl --set-version kali-linux 2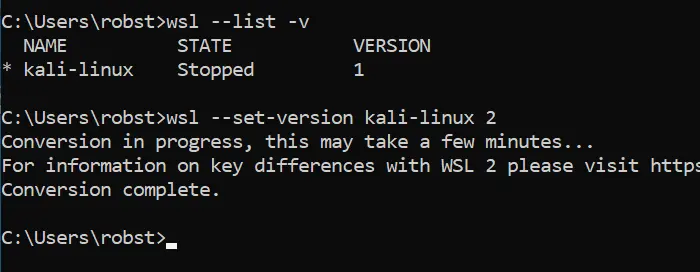
We can run the wsl --list -v command to verify that the distro was converted to WSL 2.
The client has disconnected.
with inner exception
[HttpPost]
[Route("api/Logger/Log")]
public async Task<IActionResult> Log()
{
    try
    {
        HttpHelper httpHelper = new HttpHelper();
        var requestBody = await httpHelper.GetRequestBody(Request);
        return Ok();
    }
    catch (Exception ex)
    {
        _logger.LogException(ex);
        return StatusCode(500);
    }
}
public async Task<string> GetRequestBody(HttpRequest request)
{
    using (var reader = new StreamReader(request.Body))
    {
        return await reader.ReadToEndAsync();
    }
}
[Parameters]: {}
[Exception Message]: The client has disconnected
[StackTrace]:    at Microsoft.AspNetCore.Server.IIS.Core.IO.AsyncIOOperation.GetResult(Int16 token)
   at Microsoft.AspNetCore.Server.IIS.Core.IISHttpContext.ReadBody()
   at System.IO.Pipelines.PipeCompletion.ThrowLatchedException()
   at System.IO.Pipelines.Pipe.GetReadResult(ReadResult& result)
   at System.IO.Pipelines.Pipe.ReadAsync(CancellationToken token)
   at System.IO.Pipelines.Pipe.DefaultPipeReader.ReadAsync(CancellationToken cancellationToken)
   at Microsoft.AspNetCore.Server.IIS.Core.IISHttpContext.ReadAsync(Memory`1 memory, CancellationToken cancellationToken)
   at Microsoft.AspNetCore.Server.IIS.Core.HttpRequestStream.ReadAsyncInternal(Memory`1 buffer, CancellationToken cancellationToken)
   at System.IO.StreamReader.ReadBufferAsync(CancellationToken cancellationToken)
   at System.IO.StreamReader.ReadToEndAsyncInternal()
   at OnlineBookingSystem.Utilities.HttpHelper.GetRequestBody(HttpRequest request)
   at OnlineBookingSystem.Controllers.LoggingController.Log()
[Inner Exception]: The specified network name is no longer available. (0x80070040)
[Inner StackTrace]:
Проблемы с подключением клиента Always On VPN Always On VPN client connection issues
Можно ли разрешить имя сервера удаленного доступа или VPN-адреса в адрес? Can you resolve the Remote Access/VPN server name to an IP address? В окне "Сетевые подключения" панели управления > Network Internet > Network Connectionsоткройте свойства профиля VPN. In Control Panel > Network and Internet > Network Connections, open the properties for your VPN Profile. Значение на вкладке Общие должно быть открыто разрешимым с помощью DNS. The value in the General tab should be publicly resolvable through DNS.
Можно ли получить доступ к VPN-серверу из внешней сети? Can you access the VPN server from an external network? Попробуйте открыть внешний интерфейс с помощью протокола ICMP и проверить связь с именем удаленного клиента. Consider opening Internet Control Message Protocol (ICMP) to the external interface and pinging the name from the remote client. После успешной проверки связи можно удалить правило Allow ICMP. After a ping is successful, you can remove the ICMP allow rule.
Правильно ли настроены внутренние и внешние сетевые адаптеры на VPN-сервере? Do you have the internal and external NICs on the VPN server configured correctly? Они находятся в разных подсетях? Are they in different subnets? Подключение внешнего сетевого адаптера к правильному интерфейсу в брандмауэре? Does the external NIC connect to the correct interface on your firewall?
0x80070040
ifmorrison opened this issue
Apr 8, 2016
· 13 comments
Коды ошибок Error codes
Код ошибки: 800 Error code: 800
Описание ошибки. Error description. "Удаленное подключение не удалось установить из-за сбоя использованных VPN-туннелей. The remote connection was not made because the attempted VPN tunnels failed. VPN-сервер может быть недоступен. The VPN server might be unreachable. Если это подключение пытается использовать туннель L2TP/IPsec, параметры безопасности, необходимые для согласования IPsec, могут быть настроены неправильно. If this connection is attempting to use an L2TP/IPsec tunnel, the security parameters required for IPsec negotiation might not be configured properly.
Возможная причина. Possible cause. Эта ошибка возникает, если VPN-туннель имеет тип Авто и попытка подключения завершается неудачно для всех VPN-туннелей. This error occurs when the VPN tunnel type is Automatic and the connection attempt fails for all VPN tunnels.
Возможные решения Possible solutions:
Если вы понимаете, какой туннель использовать для развертывания, задайте тип VPN на стороне VPN-клиента для этого типа туннеля. If you know which tunnel to use for your deployment, set the type of VPN to that particular tunnel type on the VPN client side.
Эта ошибка также возникает, когда не удается подключиться к VPN-серверу или не удается установить туннельное подключение. This error also occurs when the VPN server cannot be reached or the tunnel connection fails.
Проверьте следующее. Make sure:
Правильные сертификаты для IKE существуют как на клиенте, так и на сервере. The correct certificates for IKE are present on both the client and the server.
Код ошибки: 809 Error code: 809
Возможное решение. Possible solution. Убедитесь, что UDP-порты 500 и 4500 разрешены через все брандмауэры между клиентом и сервером RRAS. Ensure that UDP ports 500 and 4500 are allowed through all firewalls between the client and the RRAS server.
Код ошибки: 812 Error code: 812
Возможные причины: Possible causes:
Типичная причина этой ошибки заключается в том, что NPS указал условие проверки подлинности, которое клиент не может удовлетворить. The typical cause of this error is that the NPS has specified an authentication condition that the client cannot meet. Например, NPS может указать использование сертификата для защиты подключения PEAP, но клиент пытается использовать EAP-MSCHAPv2. For example, the NPS may specify the use of a certificate to secure the PEAP connection, but the client is attempting to use EAP-MSCHAPv2.
Журнал событий 20276 регистрируется в средстве просмотра событий, если параметр протокола проверки подлинности VPN-сервера на основе RRAS не соответствует компьютеру VPN-клиента. Event log 20276 is logged to the event viewer when the RRAS-based VPN server authentication protocol setting doesn't match that of the VPN client computer.
Возможное решение. Possible solution. Убедитесь, что конфигурация клиента соответствует условиям, указанным на сервере NPS. Ensure that your client configuration matches the conditions that are specified on the NPS server.
Код ошибки: 13806 Error code: 13806
Возможная причина. Possible cause. Эта ошибка обычно возникает, когда на VPN-сервере отсутствует сертификат компьютера или сертификат корневого компьютера. This error typically occurs when no machine certificate or root machine certificate is present on the VPN server.
Возможное решение. Possible solution. Убедитесь, что сертификаты, указанные в этом развертывании, установлены как на клиентском компьютере, так и на VPN-сервере. Ensure that the certificates outlined in this deployment are installed on both the client computer and the VPN server.
Код ошибки: 13801 Error code: 13801
Описание ошибки. Error description. Учетные данные проверки подлинности IKE недопустимы. IKE authentication credentials are unacceptable.
Сертификат компьютера, используемый для проверки IKEv2 на сервере RAS, не имеет проверки подлинности сервера в разделе " Расширенное использование ключа". The machine certificate used for IKEv2 validation on the RAS server doesn't have Server Authentication under Enhanced Key Usage.
Срок действия сертификата компьютера на сервере удаленного доступа истек. The machine certificate on the RAS server has expired.
Корневой сертификат для проверки сертификата сервера удаленного доступа отсутствует на клиентском компьютере. The root certificate to validate the RAS server certificate isn't present on the client computer.
Имя VPN-сервера, используемое на клиентском компьютере, не соответствует SubjectName сертификата сервера. The VPN server name used on the client computer doesn't match the subjectName of the server certificate.
Возможное решение. Possible solution. Убедитесь, что сертификат сервера включает проверку подлинности сервера в разделе Расширенное использование ключа. Verify that the server certificate includes Server Authentication under Enhanced Key Usage. Убедитесь, что сертификат сервера все еще действителен. Verify that the server certificate is still valid.
Убедитесь, что используемый центр сертификации указан в списке Доверенные корневые центры сертификации на сервере RRAS. Verify that the CA used is listed under Trusted Root Certification Authorities on the RRAS server. Убедитесь, что VPN-клиент подключается с помощью полного доменного имени VPN-сервера, представленного в сертификате VPN-сервера.
Verify that the VPN client connects by using the FQDN of the VPN server as presented on the VPN server's certificate.
Код ошибки: 0x80070040 Error code: 0x80070040
Описание ошибки. Error description. В сертификате сервера не используется Проверка подлинности сервера в качестве одной из записей использования сертификатов. The server certificate does not have Server Authentication as one of its certificate usage entries.
Возможная причина. Possible cause. Эта ошибка может возникать, если на сервере удаленного доступа не установлен сертификат проверки подлинности сервера. This error may occur if no server authentication certificate is installed on the RAS server.
Возможное решение. Possible solution. Убедитесь, что сертификат компьютера, используемый сервером RAS для IKEv2 , использует проверку подлинности сервера в качестве одной из записей использования сертификатов. Make sure that the machine certificate the RAS server uses for IKEv2 has Server Authentication as one of the certificate usage entries.
Код ошибки: 0x800B0109 Error code: 0x800B0109
Как правило, компьютер VPN-клиента присоединяется к домену на основе Active Directory. Generally, the VPN client machine is joined to the Active Directory-based domain. Если для входа на VPN-сервер используются учетные данные домена, сертификат автоматически устанавливается в хранилище Доверенные корневые центры сертификации.
If you use domain credentials to log on to the VPN server, the certificate is automatically installed in the Trusted Root Certification Authorities store. Однако если компьютер не присоединен к домену или используется другая цепочка сертификатов, может возникнуть эта проблема. However, if the computer is not joined to the domain or if you use an alternative certificate chain, you may experience this issue.
Описание ошибки. Error description. Цепочка сертификатов обработана, но была прервана в корневом сертификате, которому не доверяет поставщик доверия. A certificate chain processed but terminated in a root certificate that the trust provider does not trust.
Возможная причина. Possible cause. Эта ошибка может возникать, если соответствующий доверенный корневой сертификат ЦС не установлен в хранилище доверенных корневых центров сертификации на клиентском компьютере. This error may occur if the appropriate trusted root CA certificate is not installed in the Trusted Root Certification Authorities store on the client computer.
Возможное решение. Possible solution. Убедитесь, что корневой сертификат установлен на клиентском компьютере в хранилище доверенных корневых центров сертификации. Make sure that the root certificate is installed on the client computer in the Trusted Root Certification Authorities store.
Проблемы подключения при использовании условного доступа Azure AD Azure AD Conditional Access connection issues
Ой! Вы еще не можете получить доступ к этому Oops - You can't get to this yet
Возможные причины Possible cause
Сервер RADIUS (NPS) не настроен на прием только сертификатов клиентов, содержащих OID условного доступа AAD . The RADIUS server (NPS) has not been configured to only accept client certificates that contain the AAD Conditional Access OID.
В Windows PowerShell выполните командлет Get-WmiObject , чтобы создать дамп конфигурации профиля VPN. In Windows PowerShell, run the Get-WmiObject cmdlet to dump the VPN profile configuration.
Убедитесь, что разделы, и содержат правильное имя и идентификатор объекта. Verify that the , , and sections exist and shows the correct name and OID.
Появляется сообщение об ошибке "не удалось найти сертификат, который может использоваться с протоколом расширяемого протокола проверки подлинности". An error message that says "A certificate could not be found that can be used with the Extensible Authenticate Protocol" appears.
Не удалось удалить сертификат из колонки VPN-подключения Unable to delete the certificate from the VPN connectivity blade
Описание ошибки. Error description. Не удается удалить сертификаты в колонке VPN-подключения. Certificates on the VPN connectivity blade cannot be deleted.
Возможная причина. Possible cause. Для сертификата задан первичныйсертификат. The certificate is set to Primary.
Возможное решение. Possible solution.
- В колонке VPN-подключение выберите сертификат. In the VPN connectivity blade, select the certificate.
- В разделе Основнаявыберите нет, а затем нажмите кнопку сохранить. Under Primary, select No, then select Save.
- В колонке VPN-подключение снова выберите сертификат. In the VPN connectivity blade, select the certificate again.
- Нажмите кнопку Удалить. Select Delete.
Журналы NPS NPS logs
NPS создает и сохраняет журналы учета NPS. NPS creates and stores the NPS accounting logs. По умолчанию они хранятся в файлах% SYSTEMROOT% \ system32 \ \ в файле с именемXXXX. txt, где XXXX - это Дата создания файла. By default, these are stored in %SYSTEMROOT%\System32\Logfiles\ in a file named INXXXX.txt, where XXXX is the date the file was created.
По умолчанию эти журналы находятся в формате значений с разделителями-запятыми, но не содержат строки заголовка. By default, these logs are in comma-separated values format, but they don't include a heading row. Строка заголовка: The heading row is:
Если вставить эту строку заголовка в качестве первой строки файла журнала, а затем импортировать файл в Microsoft Excel, столбцы будут помечены правильно. If you paste this heading row as the first line of the log file, then import the file into Microsoft Excel, the columns will be properly labeled.
Comments
Can you try
lxrun.exe /uninstall /full
maybe this can help you
Worked great, thanks!
lxrun /uninstall /full
lxrun /uninstall /full
Type "y" to continue: y
Thanks in advance
Устранение неполадок Always On VPN Troubleshoot Always On VPN
Область применения: Windows Server (половина ежегодного канала), Windows Server 2016, Windows Server 2012 R2, Windows 10 Applies To: Windows Server (Semi-Annual Channel), Windows Server 2016, Windows Server 2012 R2, Windows 10
Если Always On установки VPN не удается подключить клиентов к внутренней сети, причиной является недопустимый сертификат VPN, неправильные политики NPS или проблемы с сценариями развертывания клиента или маршрутизацией и удаленным доступом.
If your Always On VPN setup is failing to connect clients to your internal network, the cause is likely an invalid VPN certificate, incorrect NPS policies, or issues with the client deployment scripts or in Routing and Remote Access. Первым шагом в устранении неполадок и тестировании VPN-подключения является понимание основных компонентов инфраструктуры VPN Always On.
The first step in troubleshooting and testing your VPN connection is understanding the core components of the Always On VPN infrastructure.
Устранить проблемы с подключением можно несколькими способами. You can troubleshoot connection issues in several ways. Для проблем на стороне клиента и общего устранения неполадок приложение регистрируется на клиентских компьютерах. For client-side issues and general troubleshooting, the application logs on client computers are invaluable. Для проблем, связанных с проверкой подлинности, журнал NPS на сервере NPS может помочь определить источник проблемы. For authentication-specific issues, the NPS log on the NPS server can help you determine the source of the problem.
Журналы Logs
Журналы приложений Application logs
Приложение регистрируется на клиентских компьютерах в большинстве сведений о событиях VPN-подключений более высокого уровня. The application logs on client computers record most of the higher-level details of VPN connection events.
Найдите события из источника Расклиент. Look for events from source RasClient. Все сообщения об ошибках возвращают код ошибки в конце сообщения. All error messages return the error code at the end of the message. Ниже описаны некоторые из наиболее распространенных кодов ошибок, но полный список доступен в кодах ошибок маршрутизации и удаленного доступа. Some of the more common error codes are detailed below, but a full list is available in Routing and Remote Access Error Codes.
Проблемы в работе скрипта VPN_Profile. ps1 VPN_Profile. ps1 script issues
Наиболее распространенные проблемы, возникающие при ручном запуске Profile.ps1 сценария VPN_ включают: The most common issues when manually running the VPN_ Profile.ps1 script include:
Справочник кодов ответа HTTP
Все коды 1xx-5xx: что значит, что делать посетителю и владельцу сайта.
Открыть полный инструмент